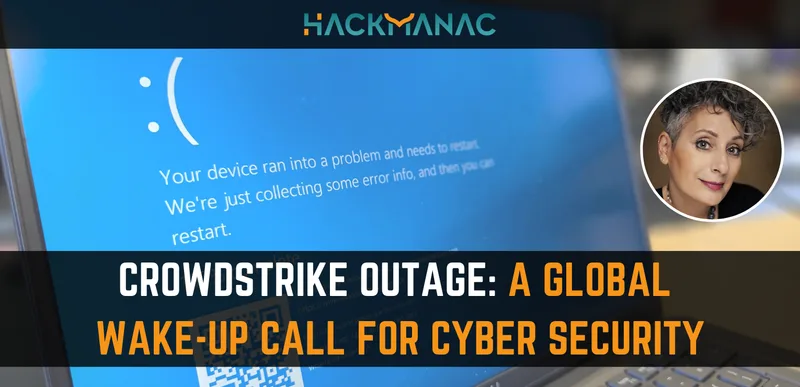
On July 19, 2024, a global IT outage caused by a faulty CrowdStrike software update sent shockwaves through critical services worldwide.
This is not the first time: in fact Crowdstrike software has reportedly been linked to crashes of Linux machines in the past.
While Microsoft has since released a free tool to help victims recover from the flawed update and Crowdstrike has provided a “remediation and guidance hub”, the incident exposed significant vulnerabilities, both technical and non-technical, in our globally interconnected digital infrastructure and highlighted the far-reaching consequences of Cyber Security failures.
This article summarizes the impact, implications and lessons learned from this event.
THE SCOPE OF THE OUTAGE
As stated by Microsoft, the CrowdStrike update malfunction affected nearly 8.5 million Windows devices, causing widespread disruptions across various sectors:
- Healthcare: surgeries and pharmacies lost access to patient records and medication dispensing systems.
- Aviation: Major airports faced significant delays, impacting global airlines and travelers. Among the victims London, Singapore, Dubai and several airports worldwide.
- Transportation: Train companies experienced outages, stranding passengers.
- Emergency Services: emergency call operators in several countries were affected.
- Media: Broadcasters like Sky News and ABC News had to suspend programs.
- Finance and Retail: Banks, stock exchanges (among them, the London Stock Exchange), and retail chains faced operational disruptions.
The domino effect of this outage underscores the critical interdependence of our digital systems and the potential for cascading failures.
CYBER SECURITY IMPLICATIONS
This incident highlights several important cyber security implications, including the fact that thousands of victims worldwide were forced to publicly disclose their reliance on CrowdStrike and Microsoft technologies.
In the aftermath, cyber criminals and other hostile actors immediately began to take advantage of the situation.
In fact, researchers have immediately found phishing and spear-phishing attacks, as well as distributed malware disguised as fixes, demonstrating the need for heightened vigilance during and after such disruptions.
Other Cyber Security considerations include:
- Vulnerabilities in Interconnected Systems: The outage exposed how a single point of failure can trigger global disruptions across multiple sectors.
- Importance of Rigorous Testing: The event highlights the need for thorough testing of software updates before deployment to prevent widespread issues.
- Disaster Recovery and Resilience: Organizations must develop robust disaster recovery plans and multiple fail-safes to quickly respond to and recover from such incidents.
- Supply Chain Security: The incident emphasizes the importance of ensuring that third-party vendors follow stringent security protocols.
- Geopolitical Dimensions: Countries less dependent on Western technology were less affected, highlighting the strategic importance of developing independent, sovereign Cyber Security measures.
FINANCIAL IMPACT AND ACCOUNTABILITY
The financial repercussions of the outage are significant:
- Affected businesses across various sectors face substantial financial losses.
- CrowdStrike may face legal challenges, reputational damage, and potential loss of customer contracts. As a result of the global outage, the company's shares reportedly dropped 13% following the incident. To apologize for the disruption, CrowdStrike even offered $10 Uber Eats gift cards to its third-party agents. But the situation is far from resolved, and it did not help that the distribution of the coupons could be mistaken for a scam.
- Insurance companies might face claims related to the disruptions, potentially leading to increased Cyber Security insurance premiums. Insurers estimated CrowdStrike’s faulty update will cost US Fortune 500 companies $5.4bn.
LESSONS LEARNED
This incident offers valuable insights for improving Cyber Security practices:
- Enhanced Testing Procedures: Implement comprehensive testing and staggered software rollouts to prevent large-scale disruptions.
- Technological Diversification: Reduce reliance on single sources of technology to mitigate strategic risks.
- Strengthened Cyber Security Strategies: Organizations must bolster their Cyber Security measures and disaster recovery plans to improve resilience against large-scale disruptions.
- Increased Vigilance: Heightened awareness and proactive measures are crucial to protect against opportunistic cyber threats in the aftermath of such incidents.
CONCLUSION
The CrowdStrike outage serves as a stark reminder of our digital vulnerabilities and the critical importance of robust Cyber Security measures.
As we navigate an increasingly interconnected world, the lessons learned from this incident must inform future strategies in IT infrastructure development, crisis management, and Cyber Security practices. The event underscores the need for continuous improvement in our approach to digital resilience and secure technological practices.
This global disruption should catalyze a renewed focus on Cyber Security at all levels – from individual organizations to national governments – to ensure we are better prepared to face and mitigate the impact of future digital crises.
Stay Cyber Safe!