Nokoyawa ransomware group re-emerged on Dark Web with a new list of victims and some peculiar behavior.
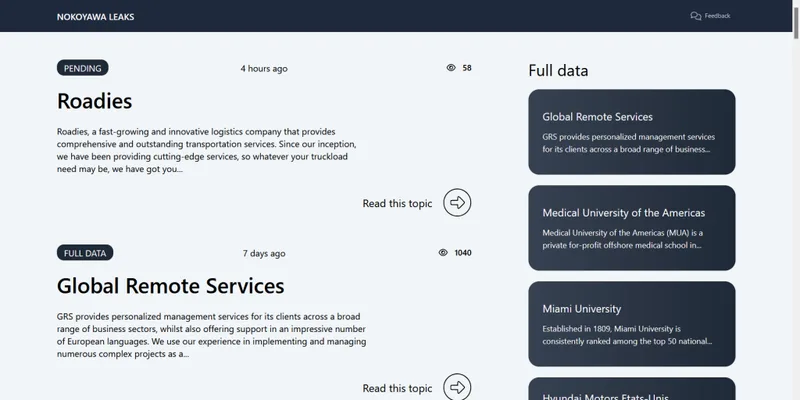
Here's what we've discovered so far.
It’s not a new ransomware group
Nokoyawa ransomware group is not new in the cybercrime scenario: in fact, it gained attention following a March 2022 report by Trend Micro, where the cybersecurity firm was originally linking their operation to the Hive ransomware family.
At the time Nokoyawa was showing similarities in Hive attack patterns and used tools.
There are connections with another group
This time the group is showing some interesting connection with Snatch, another cybercrime group.
Indeed, among the 26 victims named in Nokoyawa's DLS, it seems that 6 were also targeted by Snatch and appear among their victims:
- Gaston College
- MSX International
- City of Modesto
- Canadian Nurses Association
- Chattanooga State Community College
- Liveaction
According to Cyble The Cyber Express this may not be a coincidence but the sign of a collaboration agreement.
In any case it is certainly a reminder of the way in which criminal organizations are increasingly collaborating with each other in order to maximize the results of their operations.
They were probably relying on a 0-day
Analysing the Nokoyawa malware strain, the ransomware is targeting 64-bit Windows-based systems in double extortion attacks.
According to Kaspersky the group may have used a (at the time) zero-day vulnerability of Microsoft Windows to deploy the ransomware .
The vulnerability, identified as CVE-2023-28252, was subsequently promptly fixed and patched by Microsoft.
The victims belong to several categories
Analysing Nokoyawa victims we discovered that they belong to 12 main categories:
- Education
- Organizations
- Professional / Scientific / Technical
- ICT
- Transportation / Storage
- Gov / Mil / LE
- Construction
- Healthcare
- Manufacturing
- Wholesale / Retail
- Energy / Utilities
- Financial / Insurance
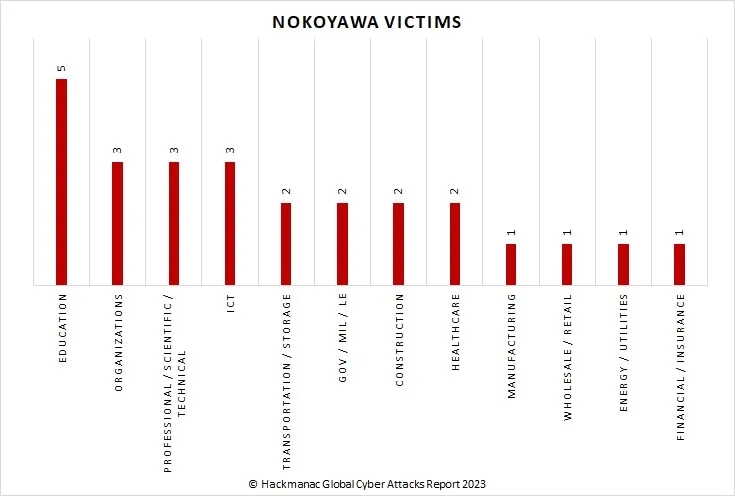
Education (19% of total attacks), Organizations, Professional / Scientific / Technical and ICT (11% each) are the most targeted categories.
Most of the victims are in America
Over two-thirds of the victims (61%) are in America, while 23% of the victims are in Europe.
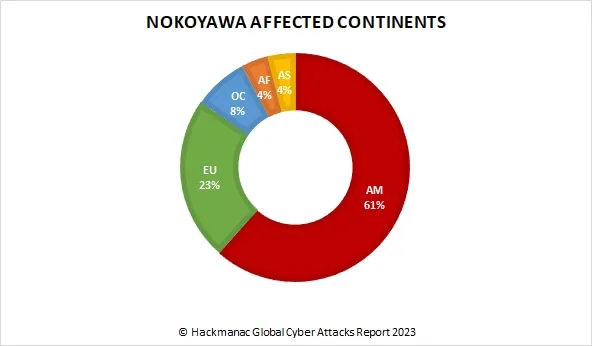
Other continents involved in Nokoyawa's attacks are Oceania (8% of attacks), Africa and Asia (4% each).
The US is the country most targeted by the group (54% of total attacks).
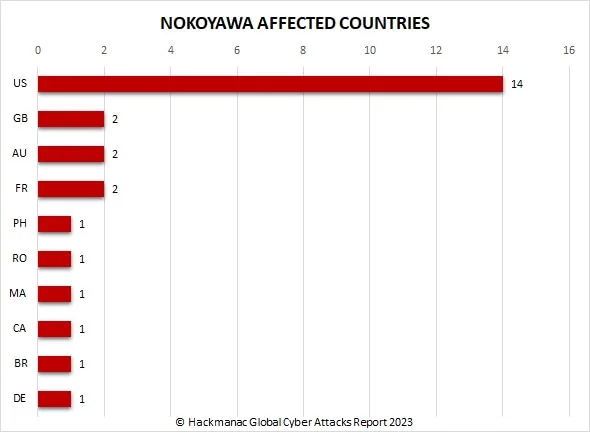
Other affected countries are:
- UK
- Australia
- France
- Philippines
- Romania
- Morocco
- Canada
- Brazil
- Germany
They're speeding up
We detected 26 victims of Nokoyawa in 2023, 5.2 per month on average.
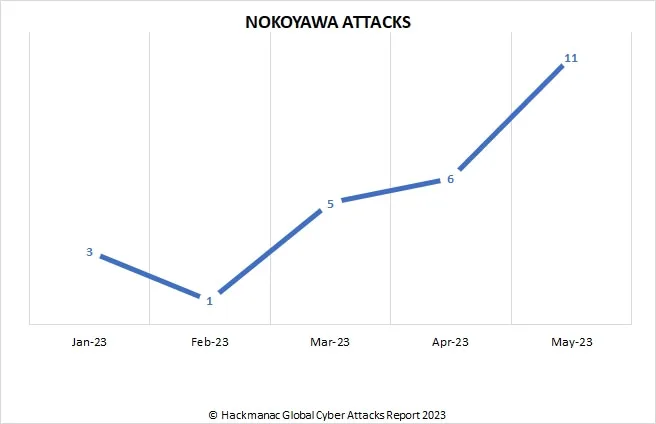
The attacks, which started quietly in the first months of the year, grow decisively in May where we already have 11 attacks in the group's assets.
Ultimately Nokoyawa appears to be a particularly dangerous ransomware group.
On the one hand, the group has clearly demonstrated that it can count on several criminal associations that appear to have been beneficial.
On the other hand, Nokoyawa's double extortion operations seem to be accelerating.
In this case, our recommendation is to update and keep secure the information systems, especially those based on Windows.
Stay Cyber Safe!