My view after 20+ years in cybersecurity: four assumptions keep us exposed, and correcting them turns cyber risk into an informed business decision.
Read More
The WereWolves ransomware group has been recently added to our database, and a first look at it’s data leak site reveals that 21 victims have been listed; 14 located in Russia along with another 7 across the USA, France, Netherlands, Germany, Serbia and Macedonia, apparently targeted between May 18th and November 2nd, 2023.
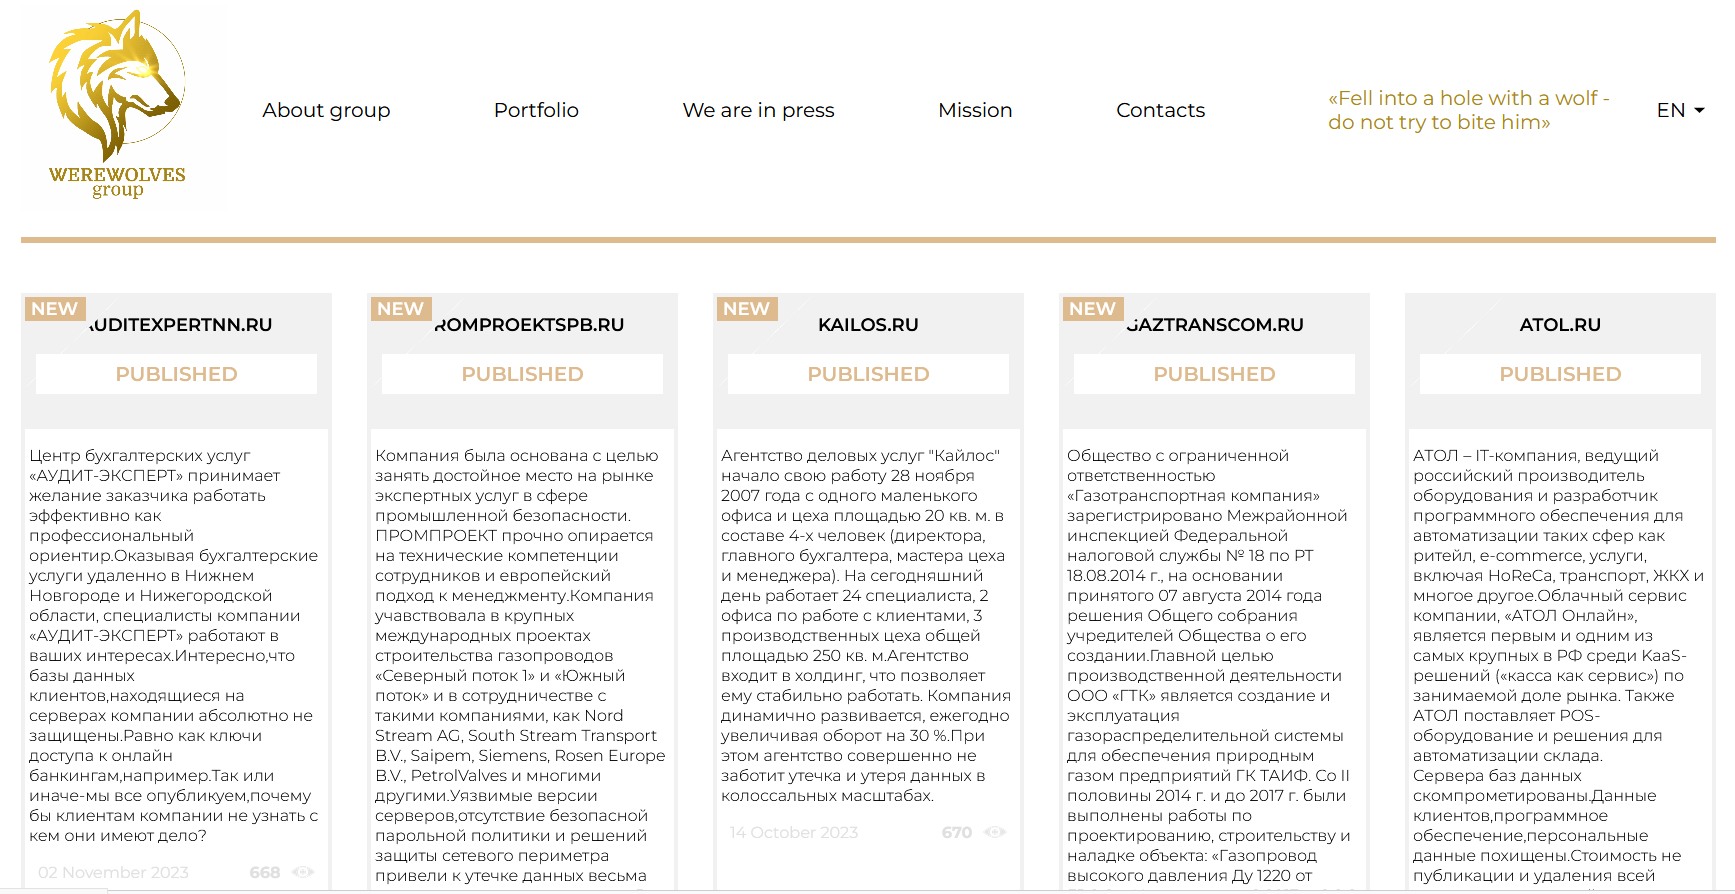
In the “About Us” section, the group portrays itself as an organization committed to cyber attacks and ransomware operations, offering tailored negotiations for data recovery while threatening of punitive measures if agreements are not met. Their “Mission” section states the following: “We see our mission in strengthening the cyber immunity of companies around the world, and this is definitely worth the money.”
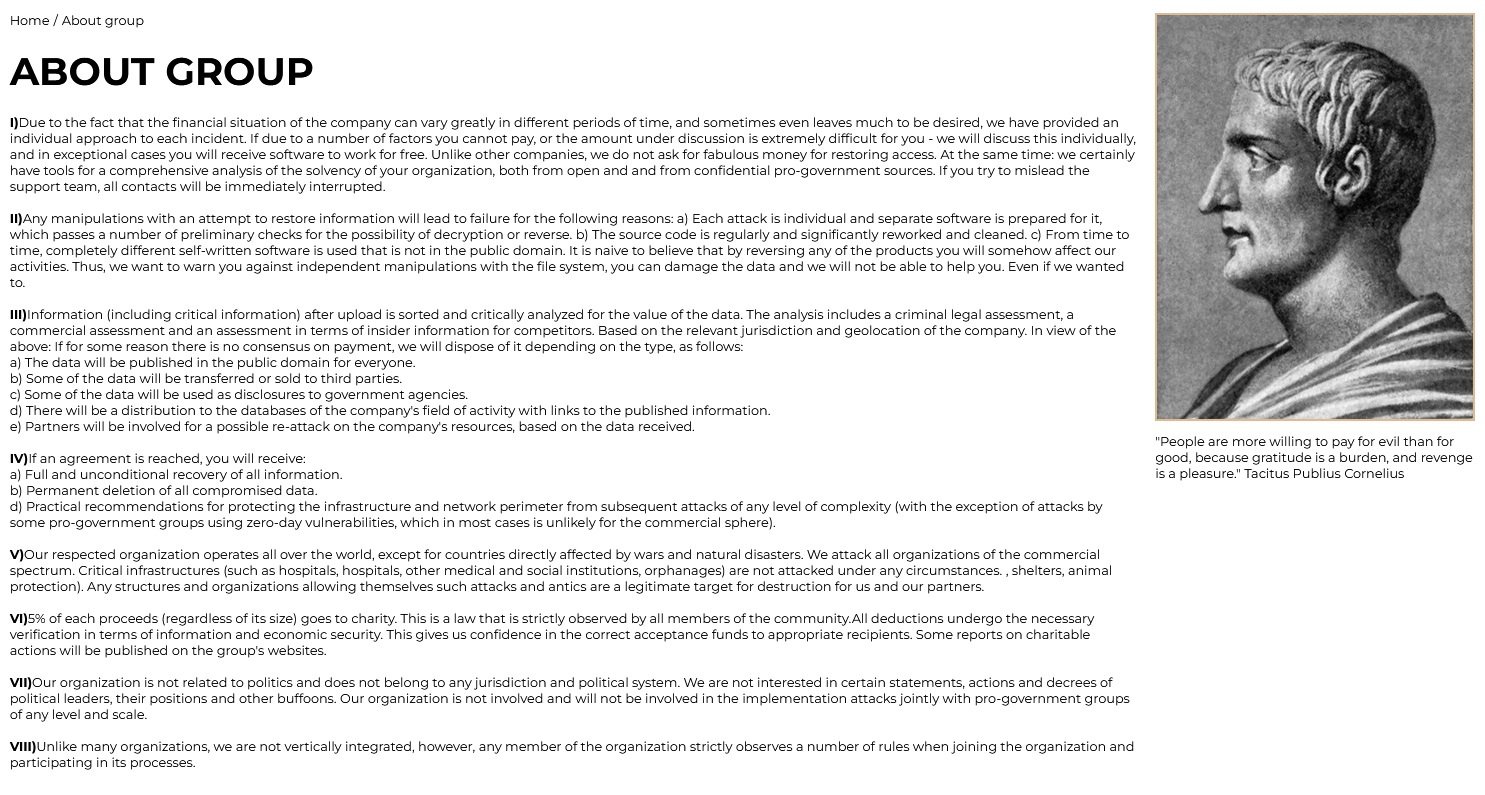
Additionally, they feature a “Portfolio” section inviting security researchers, ethical, and unethical hackers worldwide to join their bug-finding bounty program. This program focuses on website vulnerabilities, doxing, software vulnerabilities, TOX vulnerabilities, unique ideas, and TOR vulnerabilities, with bounties ranging from $1,000 to $1 million.
Seeking public attention, the cybercrime group has published a 2022 article from Ghana Business News, claiming responsibility for an attack on the Electricity Company of Ghana (ECG). Following a ransomware attack, ECG was reportedly unable to buy power, resulting in several days of power outages.
Their blog also includes a recruitment call for new members with hacking skills. They promise flexible working hours, regular salary, and training, targeting both seasoned hackers and those with knowledge but less practical experience. A deposit of 1 Bitcoin is required as a security measure to deter unsuitable candidates like law enforcement or journalists. Applicants must demonstrate their hacking prowess and readiness to commit to cyber attacks immediately upon joining, with the organization emphasizing a structured recruitment process focused on skills, experience, and dedication to their illicit activities.
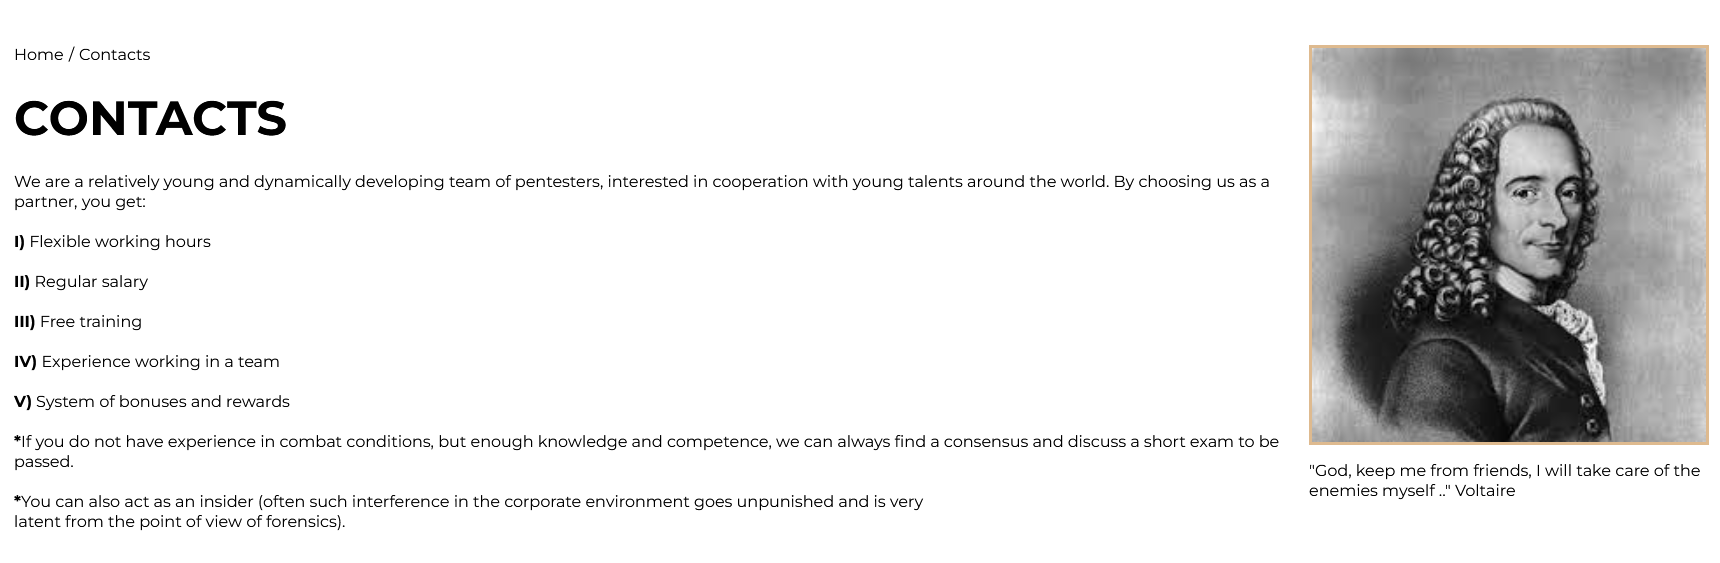
Although the last recorded activity was on November 2nd, by looking at the timeline of their attacks the group is likely to be still active, requiring a continuous monitoring.
An analysis of the attacks published by WereWolves provides us with an overview of the types of targets affected:
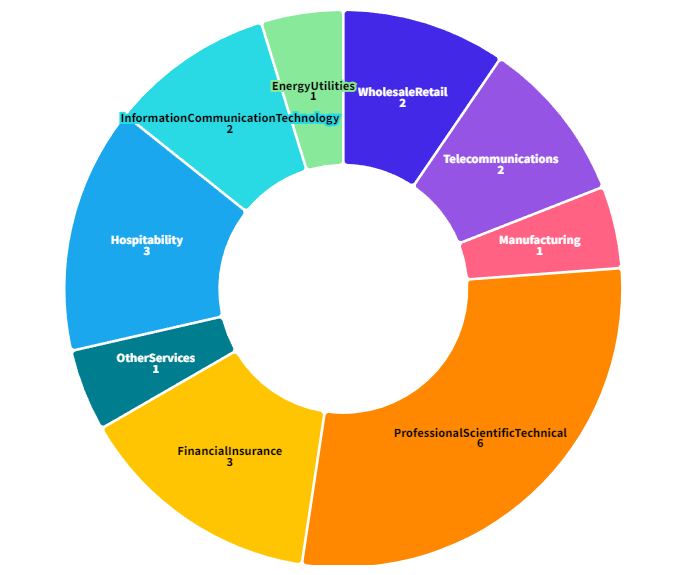
With 28.6%, the Professional/Scientific/Technical sector secures the leading position, closely followed by both the Financial/Insurance and Hospitality sectors, each holding a share of 14.3%. Subsequent to these are the WholesaleRetail, Telecommunications, and InformationCommunicationTechnology sectors, each accounting for 9.5%. Finally, the Manufacturing, EnergyUtilities, and OtherServices sectors each comprise 4.7%.
Interestingly, among the victims listed on the blog, 6 appear to be copy-pasted from attacks previously conducted by LockBit (Agency for Electronic Communications, Metalnet, Interfides, La Poste Mobile, Emprint, Big Centers). The posts for these 6 victims indeed showcase identical samples and the same amount of data exfiltrated.
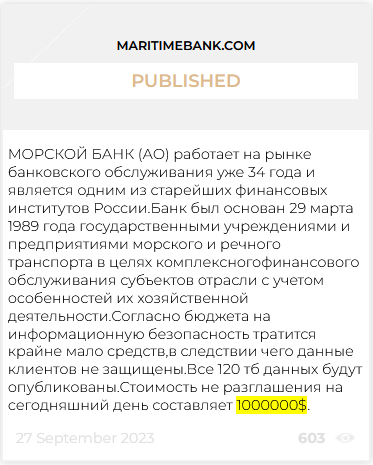
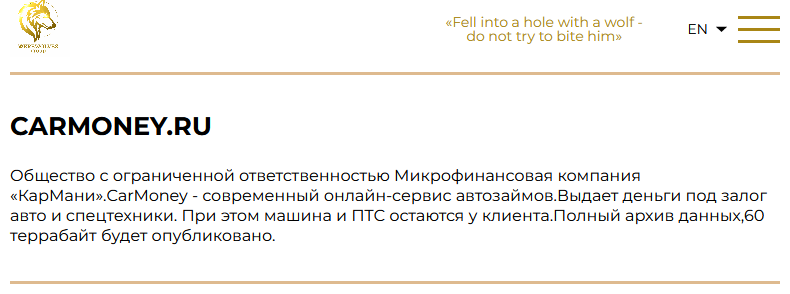
Other impacted companies have captured our attention, this time for the extreme quantity of data that WereWolves claims to have exfiltrated. In the post detailing the attack on Maritime Bank, the cybercriminals assert that they have exfiltrated 120 Terabytes of data, and for CarMoney, 60 Terabytes. This volume of data is rarely seen even among the largest criminal organizations. As always, these statements are pending confirmation.
According to experts from the Digital Forensics Laboratory of F.A.C.C.T., the ransomware group WereWolves primarily targets victims’ poorly protected public services as their initial attack vector. They encrypt company data using a version of the LockBit3 (Black) ransomware program. This particular version is compiled from a builder that has surfaced in the public domain. In their operations, WereWolves also utilize the leaked tools of the notorious cybercriminal group Conti, known for having over 850 victims including corporations, and government agencies.
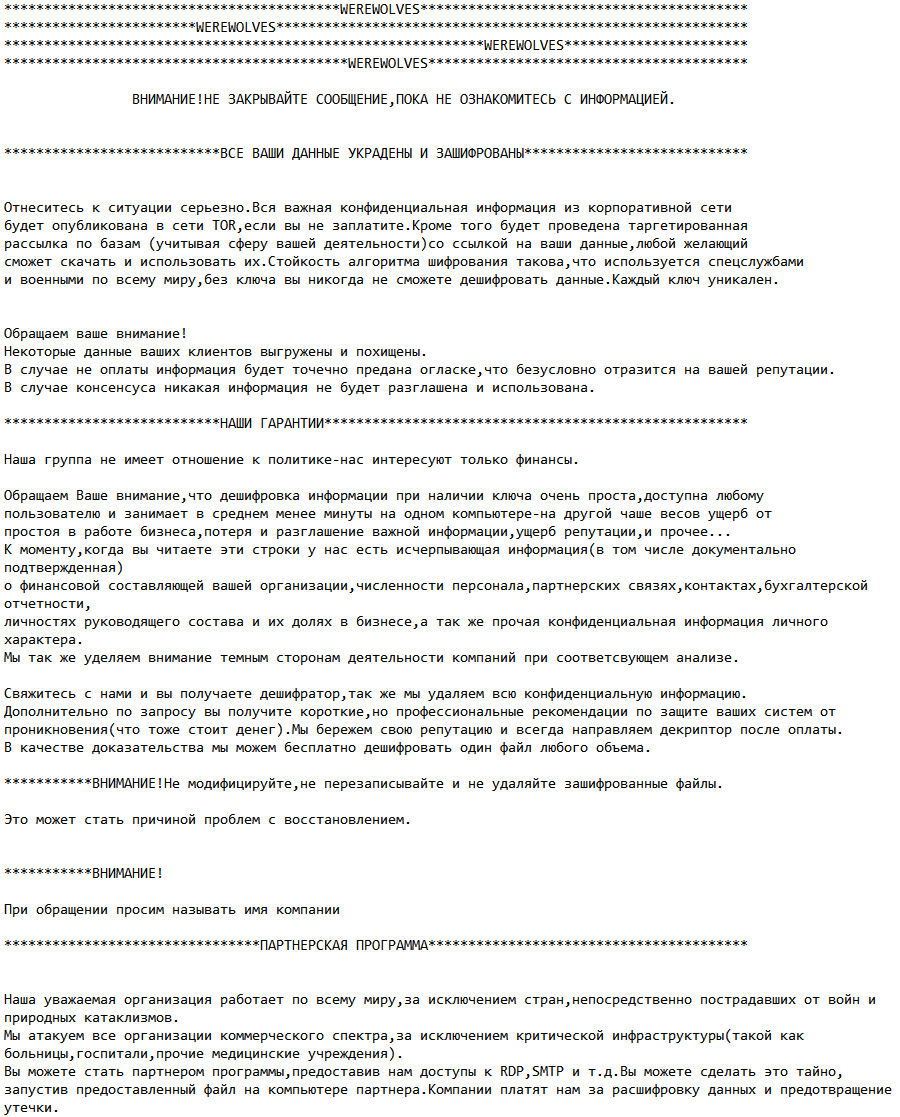
Furthermore, WereWolves is known for its adoption of the ‘double extortion‘ tactic. This approach involves not only demanding a ransom for the decryption of data but also posting sensitive data about non-compliant victim companies on their own Data Leak Site (DLS).
BIG Centers, Agency for Electronic Communications, Metalnet, Interfides, Easy Loan, QB2B, Emprint, La Poste Mobile, acac Fitness & Wellness, AMAKS Hotels & Resorts, Aurora Store, AMAKS Congress Hotel Khabarovsk, Maritime Bank, CROC Incorporated, CarMoney, RoomHotel, ATOL, Gas Transportation Company, Kailos, Promproekt, Audit-Expert.
Confirmation or denial of WereWolves’ attacks would be a decisive factor in assessing the actual threat posed by this ransomware group, which until now has remained in the shadows. Moreover, given the 6 attacks coinciding with those of LockBit, an affiliation between the two criminal gangs cannot be ruled out. Continuous monitoring will reveal the true nature of WereWolves.
Victim website: | bigcenters.rs |
Victim country: | Serbia |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | N/A |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | Financial documents |
Leaked data: | 100% of the exfiltrated data |
Ransom deadline: | Expired |
Cyber Risk Factor: | 4 |
Image: |
|
Victim website: | aek.mk |
Victim country: | Macedonia |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | N/A |
Exfiltrated data amount: | 118 GB |
Exfiltrated data type: | Financial documents, PII, credit cards, etc. |
Leaked data: | 100% of the exfiltrated data |
Ransom deadline: | Expired |
Cyber Risk Factor: | 4 |
Image: |
|
Victim website: | metalnet.nl |
Victim country: | Netherlands |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | N/A |
Exfiltrated data amount: | 49 GB |
Exfiltrated data type: | Technical designs, invoices and financial documents, etc. |
Leaked data: | 100% of the exfiltrated data |
Ransom deadline: | Expired |
Cyber Risk Factor: | 4 |
Image: |
|
Victim website: | interfides.de |
Victim country: | Germany |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | N/A |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | Projects, financial data, etc. |
Leaked data: | 100% of the exfiltrated data |
Ransom deadline: | Expired |
Cyber Risk Factor: | 4 |
Image: |
|
Victim website: | lzaim38.ru |
Victim country: | Russia |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | $ 45,000 |
Exfiltrated data amount: | Miscellaneous documents including passports and photos, etc. |
Exfiltrated data type: | N/A |
Leaked data: | 100% of the exfiltrated data |
Ransom deadline: | Expired |
Cyber Risk Factor: | 4 |
Image: |
|
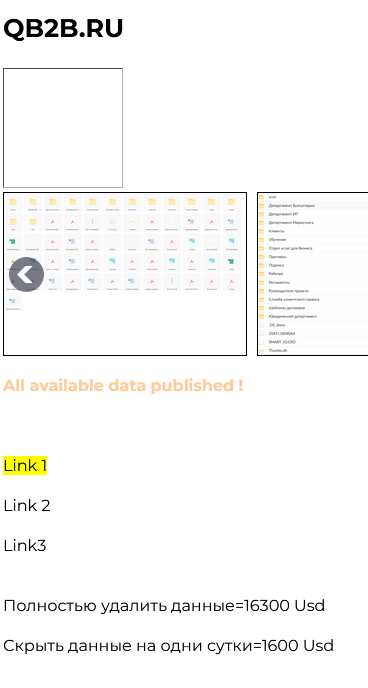
Victim website: | qb2b.ru |
Victim country: | Russia |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | $ 16,300 |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | Miscellaneous documents including scans and passports, etc. |
Leaked data: | 100% of the exfiltrated data |
Ransom deadline: | Expired |
Cyber Risk Factor: | 4 |
Image: |
|
Victim website: | emprint.com |
Victim country: | USA |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | N/A |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | N/A |
Leaked data: | / |
Ransom deadline: | Expired |
Cyber Risk Factor: | 2 |
Image: |
|
Victim website: | lapostemobile.fr |
Victim country: | France |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | N/A |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | N/A |
Leaked data: | / |
Ransom deadline: | Expired |
Cyber Risk Factor: | 3 |
Image: |
|
Victim website: | acac.com |
Victim country: | USA |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | N/A |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | N/A |
Leaked data: | / |
Ransom deadline: | Expired |
Cyber Risk Factor: | 2 |
Image: |
|
Victim website: | krasnoyarsk.amaks |
Victim country: | Russia |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | $ 4,000 |
Exfiltrated data amount: | 1.0 TB |
Exfiltrated data type: | Miscellaneous documents including videos and photos, etc. |
Leaked data: | 100% of the exfiltrated data |
Ransom deadline: | Expired |
Cyber Risk Factor: | 4 |
Image: |
|
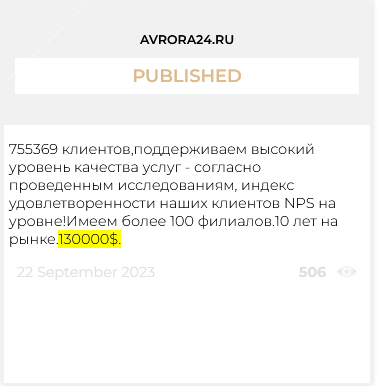
Victim website: | avrora24.ru |
Victim country: | Russia |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | $ 130,000 |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | N/A |
Leaked data: | / |
Ransom deadline: | Expired |
Cyber Risk Factor: | 2 |
Image: |
|
Victim website: | habarovsk.amaks |
Victim country: | N/A |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | $ 3,000 |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | Miscellaneous documents including videos and photos, etc. |
Leaked data: | 100% of the exfiltrated data |
Ransom deadline: | Expired |
Cyber Risk Factor: | 4 |
Image: |
|
Victim website: | maritimebank.com |
Victim country: | Russia |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | $ 1,000,000 |
Exfiltrated data amount: | 120 TB |
Exfiltrated data type: | Clients’ data |
Leaked data: | / |
Ransom deadline: | Expired |
Cyber Risk Factor: | 5 |
Image: |
|
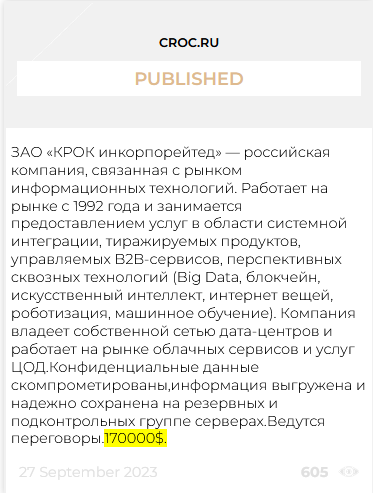
Victim website: | croc.ru |
Victim country: | Russia |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | $ 170,000 |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | N/A |
Leaked data: | / |
Ransom deadline: | Expired |
Cyber Risk Factor: | 4 |
Image: |
|
Victim website: | carmoney.ru |
Victim country: | Russia |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | N/A |
Exfiltrated data amount: | 60 TB |
Exfiltrated data type: | N/A |
Leaked data: | / |
Ransom deadline: | Expired |
Cyber Risk Factor: | 5 |
Image: |
|
Victim website: | roomhotel-sochi.ru |
Victim country: | Russia |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | N/A |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | N/A |
Leaked data: | / |
Ransom deadline: | Expired |
Cyber Risk Factor: | 2 |
Image: |
|
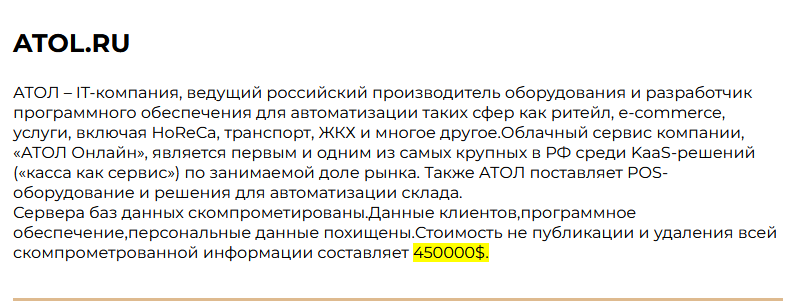
Victim website: | atol.ru |
Victim country: | Russia |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | $ 450,000 |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | Database, clients’ data, personal data, software data, etc. |
Leaked data: | 100% of the exfiltrated data |
Ransom deadline: | Expired |
Cyber Risk Factor: | 5 |
Image: |
|
Victim website: | gaztranscom.ru |
Victim country: | Russia |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | $ 60,000 |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | Clients’ data |
Leaked data: | 100% of the exfiltrated data |
Ransom deadline: | Expired |
Cyber Risk Factor: | 4 |
Image: |
|
Victim website: | kailos.ru |
Victim country: | Russia |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | $ 6,000 |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | Miscellaneous documents |
Leaked data: | 100% of the exfiltrated data |
Ransom deadline: | Expired |
Cyber Risk Factor: | 4 |
Image: |
|
Victim website: | promproektspb.ru |
Victim country: | Russia |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | N/A |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | Clients’ data |
Leaked data: | / |
Ransom deadline: | Expired |
Cyber Risk Factor: | 4 |
Image: |
|
Victim website: | auditexpertnn.ru |
Victim country: | Russia |
Attacker name: | WereWolves |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | N/A |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | Clients’ data |
Leaked data: | / |
Ransom deadline: | N/A |
Cyber Risk Factor: | 3 |
Image: |
|
Stay Cyber Safe!
My view after 20+ years in cybersecurity: four assumptions keep us exposed, and correcting them turns cyber risk into an informed business decision.
Read MoreHACK TUESDAY WEEK 09 - 15 SEPTEMBER 2026: 445 CYBERATTACKS ACROSS 74 COUNTRIES
Read MoreHACK TUESDAY WEEK 09 - 15 SEPTEMBER 2026: 445 CYBERATTACKS ACROSS 74 COUNTRIES
Read More
					-----BEGIN PGP PUBLIC KEY BLOCK-----

xjMEZvKNjxYJKwYBBAHaRw8BAQdAY0FqtSiDPx0W2I/TcbueKG6Rgc/MZ39sAe4M
pf+96qrNJ2luZm9AaGFja21hbmFjLmNvbSA8aW5mb0BoYWNrbWFuYWMuY29tPsKM
BBAWCgA+BYJm8o2PBAsJBwgJkBE5t99Xp+hGAxUICgQWAAIBAhkBApsDAh4BFiEE
mgd0+HpNd7RcUR8jETm331en6EYAAKaRAQCPZ/LvREX19qlSpoYdfyD9qZYbhF8y
BxXDDkgntOnTXgD/ZXMY7/15tkm/NS3/9vmugseZq9x1y6LCVoua8RTEjALOOARm
8o2PEgorBgEEAZdVAQUBAQdA687+KKGub0wBlfH39ll+dqUZufUavN4OJD6jcJ1i
KGwDAQgHwngEGBYKACoFgmbyjY8JkBE5t99Xp+hGApsMFiEEmgd0+HpNd7RcUR8j
ETm331en6EYAACkcAQCRg9BZDGbluQdtGNlrFg9PpAQBkdDg2Rcso06B9tPchAEA
27bGmaKz9zrUwWq7tq4N8jXWdxexefiKcK3+4BGSGA0=
=OEQG
-----END PGP PUBLIC KEY BLOCK-----