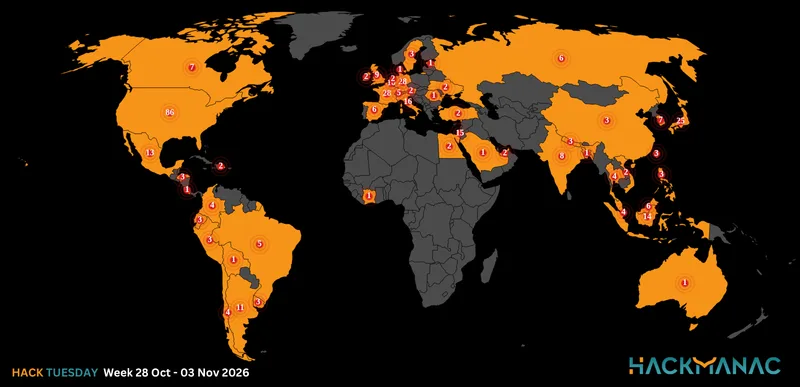
Today's HOT includes 9 victims by the notorious The Five Families, Cuba, Akira, Play, BianLian and LockBit 3.0 gangs.
The average Cyber Risk Factor is 4.0.
Read below the full list.
Disclaimer:
Data are collected from public info published on Dark Web.
The Cyber Risk factor is calculated on cyber attacks' impact based on available data.
It shows the severity of an event: 1 = low, 5 = critical
ABEL SANTOS Y ASOCIADOS
Victim website: | abelsantosyasoc.com.ar |
Victim country: | Argentina |
Attacker name: | The Five Families |
Attacker class: | Cybercrime |
Attack technique: | Data breach |
Ransom demand: | N/A |
Exfiltrated data amount: | 200 GB |
Exfiltrated data type: | N/A |
Leaked data: | Sample |
Ransom deadline: | 14th Feb 24 |
Cyber Risk Factor: | 4 |
Image: |
|

MANCHESTER FERTILITY
Victim website: | manchesterfertility.com |
Victim country: | United Kingdom |
Attacker name: | LockBit 3.0 |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | N/A |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | N/A |
Leaked data: | / |
Ransom deadline: | 12th Feb 24 |
Cyber Risk Factor: | 4 |
Image: |
|

STEMCOR
Victim website: | stemcor.com |
Victim country: | United Kingdom |
Attacker name: | LockBit 3.0 |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | N/A |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | N/A |
Leaked data: | / |
Ransom deadline: | 21st Feb 24 |
Cyber Risk Factor: | 3 |
Image: |
|

GATES SHIELDS
Victim website: | gatesshields.com |
Victim country: | USA |
Attacker name: | LockBit 3.0 |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | $ 59,999 |
Exfiltrated data amount: | 400 GB |
Exfiltrated data type: | Data of more than 1000 clients: Personal data, addresses, telephone numbers, SSN, EIN. Types of documents: Customer loan agreements, real estate documents, wills, police arrest reports, court cases, mail correspondence with company employees, as well as internal mail correspondence, as well as financial documents of the company and its employees, including one state senator |
Leaked data: | Sample |
Ransom deadline: | 4th Feb 24 |
Cyber Risk Factor: | 5 |
Image: |
|

DMS IMAGING
Victim website: | dms-imaging.com |
Victim country: | France |
Attacker name: | Cuba |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | N/A |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | Financial documents, correspondence with bank employees, account movements, balance sheets, tax documents, compensation, source code. |
Leaked data: | Fully published |
Ransom deadline: | N/A |
Cyber Risk Factor: | 4 |
Image: |
|

BORAH, GOLDSTEIN, ALTSCHULER, NAHINS & GOIDEL
Victim website: | borahgoldstein.com |
Victim country: | USA |
Attacker name: | Akira |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | N/A |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | Miscellaneous documents including clients and projects’ data |
Leaked data: | / |
Ransom deadline: | N/A |
Cyber Risk Factor: | 3 |
Image: |
|

INNOVEX DOWNHOLE SOLUTIONS
Victim website: | innovex-inc.com |
Victim country: | USA |
Attacker name: | Play |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | N/A |
Exfiltrated data amount: | N/A |
Exfiltrated data type: | Private and personal confidential data, clients’ documents, budget, IDs, payroll, insurance, taxes, finance information and etc. |
Leaked data: | / |
Ransom deadline: | 04th Feb 24 |
Cyber Risk Factor: | 4 |
Image: |
|

LAW OFFICE OF MICHAEL H. JOSEPH
Victim website: | newyorktriallawyers.org |
Victim country: | USA |
Attacker name: | BianLian |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | N/A |
Exfiltrated data amount: | 1.9 TB |
Exfiltrated data type: | Finance data, HR data, clients' and customers' confidential data, incidents and cases, court and police files, clients' health and medical records, internal and external email correspondence, cases' images, and videos |
Leaked data: | / |
Ransom deadline: | N/A |
Cyber Risk Factor: | 5 |
Image: |
|

TANDEM
Victim website: | tandemlasvegas.com |
Victim country: | USA |
Attacker name: | BianLian |
Attacker class: | Cybercrime |
Attack technique: | Ransomware |
Ransom demand: | N/A |
Exfiltrated data amount: | 2 TB |
Exfiltrated data type: | Financial data, HR data, clients' and partners' data, projects, mailboxes, internal and external email correspondence. |
Leaked data: | / |
Ransom deadline: | N/A |
Cyber Risk Factor: | 5 |
Image: |
|

Stay safe!
Hackmanac Team!